When discussing cybersecurity, most strategies naturally focus on software to gain flexibility. Software solutions enable continuous updates to patch new threats exploited by cyberattacks. Yet there is a more fundamental question that receives far less attention:
Can the Device Itself Be Trusted?
Europe is preparing the transition to post-quantum cryptography of digital systems, an important question is emerging: how can we trust the devices that integrate those cryptographic algorithms in the first place?
This is where Hardware Roots of Trust (HRoTs) enter the picture.
Real Trusted Devices?
Imagine a diamond protected by the world’s strongest lock. The lock may be impossible to break, but what if someone secretly swapped the diamond for another one before it was locked away?
The same principle applies to digital systems. Encryption can protect communications, but if an attacker compromises a device before it sends or receives information, even the strongest cryptography may not help.
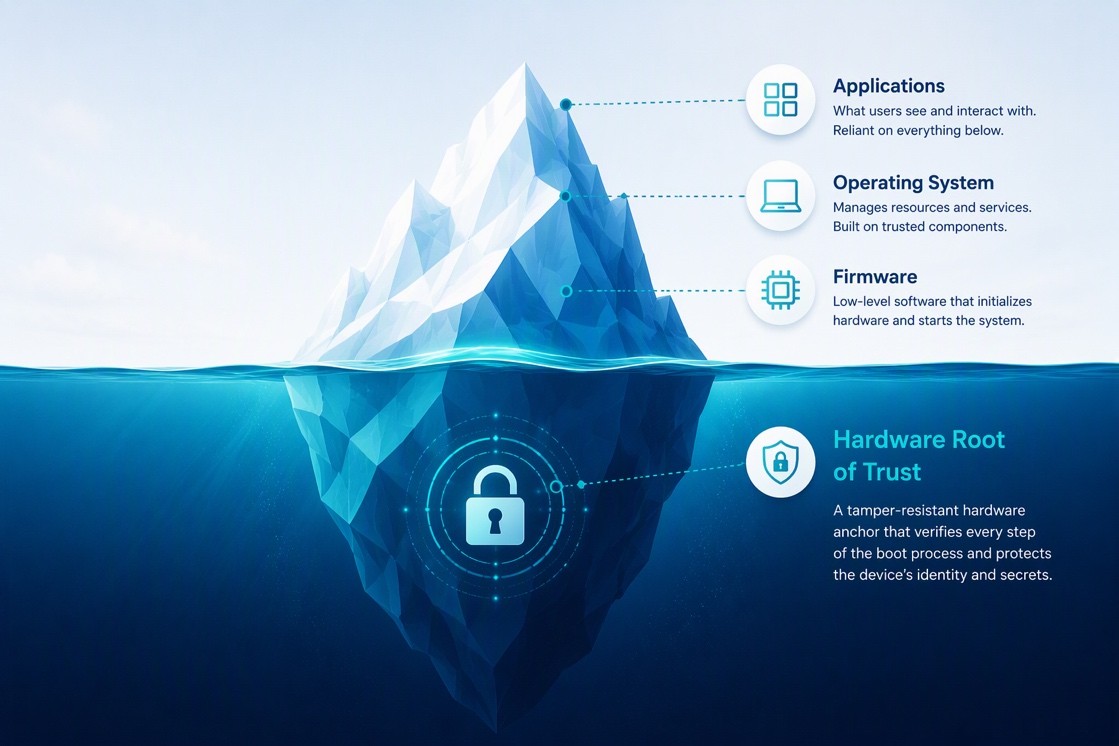
Most security mechanisms are visible above the surface… But trust relies on underlying layers.
The Digital Equivalent of a Human Identity
A HRoT is the core to anchor the device’s original proof of identity. Just as a number in an identity card provides a trusted way to verify a person’s identity, a HRoT preserves the integrity of a device. When a system powers on, the HRoT verifies whether the firmware has been altered. The firmware then verifies the next software component, which in turn verifies the next one, creating what security engineers call a chain of trust. If everything checks out, the device continues to boot normally. If something has been modified unexpectedly, the process can be interrupted before potentially malicious code is executed. In the case of the diamond, you could use a microscope to verify that it is the original diamond and has not been swapped. Only then would you lock the safe. This idea may sound simple, but it has become one of the most important principles in modern cybersecurity.
Why Trust Starts Before Software Runs
Most users assume that a device becomes operational when the operating system starts. In reality, several critical steps take place long before that moment. Hardware components are initialized, firmware is executed, and security checks are performed before the operating system is even loaded. These early verification stages form the foundation of the chain of trust and help ensure that the device starts from a known and trusted state.
The Future of Secure Devices
Today’s digital world includes critical areas as finance, healthcare, smart cities, satellite communications, and enterprise networks. In these environments, device identity and integrity are becoming strategic concerns in security. The quantum menace demands the integration of quantum-resistant mechanisms to protect these devices. A holistic approach is required to provide a quantum-resistant infrastructure with end-to-end trusted devices. This is why Q-FENCE investigates the combination of complementary technologies, including hardware-assisted security based on HRoT and post-quantum cryptography accelerators, quantum source entropy, secure boot and attestation mechanisms. As connected systems become increasingly integrated into our lives, the ability to establish trust from the hardware upwards may become one of the most important security capabilities of all.